A DataOps Article.
What Is the Consumer Data Right (CDR)?
You may have heard it mentioned, particularly if you’re in “Open Banking”. But CDR is the future of how we access and ultimately share our data with “trusted” third parties.
It started in the Australian banking sector in mid-2020. From there, the plan was to expand its scope in phases and eventually roll it out to other sectors of the economy, including superannuation, energy and telecommunications.
Vendor Benefits
The Consumer Data Right is a competition and consumer reform first!
- Reduced sector “monopolization” (increased competition).
- CDR encourages innovation and competition between service providers.
- Access to new digital products & channels.
- New and innovative customer experiences.
Consumer Benefits
- Immediate access to your information for quicker decision making.
- Better transparency of vendor(s) pricing and offers.
- Increase in products to support your lifestyle.
- Consumer power e.g. ease of switching when dissatisfied with providers.
Vendor Risks
- CDR Compliance is mandatory for Data Holders
- Implementing CDR (on top of legacy platforms) is non-trivial.
- Non-compliance penalties may be severe (fines and trading restrictions)
- CDR is rapidly evolving & continually changing. Continuous conformance validation & upkeep required.
- Increased access to data, means increased “attack footprint”.
Be warned! Although the CDR should create exciting new opportunities, there are also clearly defined conformance requirements. In a nutshell, breaches of the CDR Rules can attract severe penalties ranging from $10M to 10% of the organization’s annual revenue. Data holders must also protect customer data outside production. For practical guidance, see supporting privacy regulations in non-production and how to secure non-production data.
Who Is Responsible for the CDR?
Ultimately, CDR may evolve to a point where it is self-regulating. However, for now at least, the relevant industry regulators control the accreditation of who can be part of the ecosystem (i.e. Data Holders & Data Recipients)*.
*In Australia the ACCC is responsible for implementing the CDR system. Only accredited organisations can provide services in the CDR system. An accredited provider must comply with a set of privacy safeguards, rules and IT system requirements that protect your privacy and keep your data secure in transit and in storage.
How Do Consumers Keep Their Data Safe?
As a result, service providers only get your data after you authenticate and give consent.
Note: The diagram below, based on Australian oAuth2/OIDC security CDR guidelines, shows the key interactions between the Consumer, The Data Recipient (e.g. a Retailer App on a Phone) and a Data Holder (a Bank).
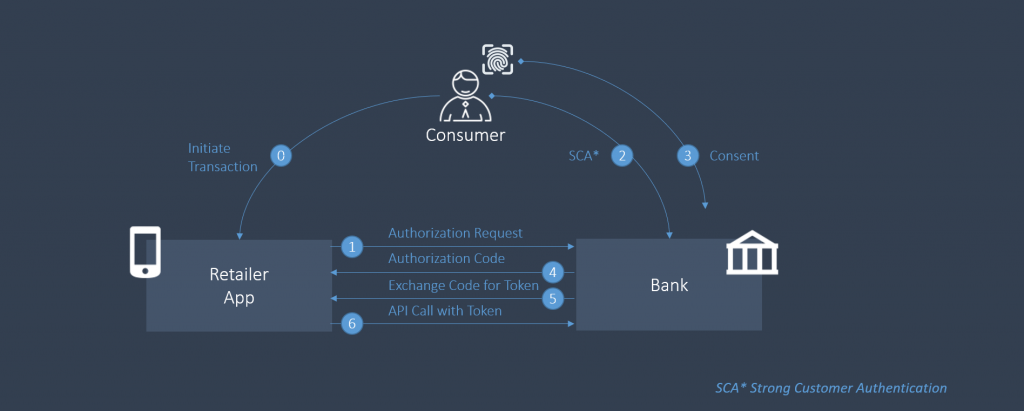
Australian CDR uses oAuth2/OIDC Hybrid Flow
Consumers can control what data is shared, what it can be used for and for how long. In addition, consumers can revoke consent and request deletion of their information at any time.
CDR is the beginning of an interesting new information era. Learn more about the Consumer Data Right and accreditation on the CDR website.